Start with the control chain
Microsoft Purview provides connected capabilities, but each solves a different part of the problem:
- Discover and classify: Identify sensitive content through built-in or custom detectors.
- Label and protect: Express sensitivity and, when needed, apply markings, access restrictions, or encryption.
- Prevent loss: Use DLP policies to evaluate an action and respond with audit, coaching, override, restriction, or blocking.
- Observe and investigate: Review activities, alerts, audit evidence, and policy outcomes.
- Improve: Tune detection, scope, actions, and exceptions as the business and threat landscape change.
Do not treat these as interchangeable features. A sensitive information type detects content. A sensitivity label classifies an item and may protect it. A DLP policy evaluates conditions and controls an activity.
How Microsoft Purview identifies data
Sensitive information types
Sensitive information types, often shortened to SITs, detect recognizable data such as identifiers, financial values, or credentials. Detection can use patterns, keywords, validation functions, proximity, and confidence levels. Built-in SITs accelerate common scenarios, while custom SITs can represent organization-specific formats.
Use higher confidence and supporting evidence for disruptive controls. A low-confidence match may be useful for discovery but too noisy for a hard block.
Exact Data Match
Exact Data Match can identify known sensitive records from an approved reference data set with greater precision than a general pattern. It is useful when the organization needs to protect its actual customer, patient, or employee records rather than every value with a similar format.
Document fingerprinting
Document fingerprinting recognizes documents derived from a standard form or template. It can help protect completed application forms, standard contracts, or other structured documents whose layout is more meaningful than one field.
Trainable classifiers
Trainable classifiers identify categories based on representative content rather than only fixed patterns. They are useful for concepts such as business documents or subject matter that varies in wording. They require good examples, validation, and periodic review.
Microsoft describes these classification approaches in its classifier overview. Feature support differs by workload and condition, so verify a detector against the target location before relying on it.
Sensitivity labels
Sensitivity labels let organizations classify files, email, and supported containers. Depending on configuration and workload, a label can:
- display a header, footer, or watermark
- apply encryption and usage restrictions
- influence sharing and access settings
- provide a signal for DLP and reporting
- remain associated with supported content as it moves
Keep the label model understandable. Labels should correspond to handling decisions, not reproduce an internal policy manual. Microsoft maintains current capabilities and deployment considerations in Learn about sensitivity labels.
Microsoft Purview DLP
DLP policies combine four elements:
- Location: Where the policy applies.
- Condition: What content or context creates a match.
- Action: What the service audits, warns about, restricts, or blocks.
- User and administrator response: Policy tips, overrides, incident reports, and alerts.
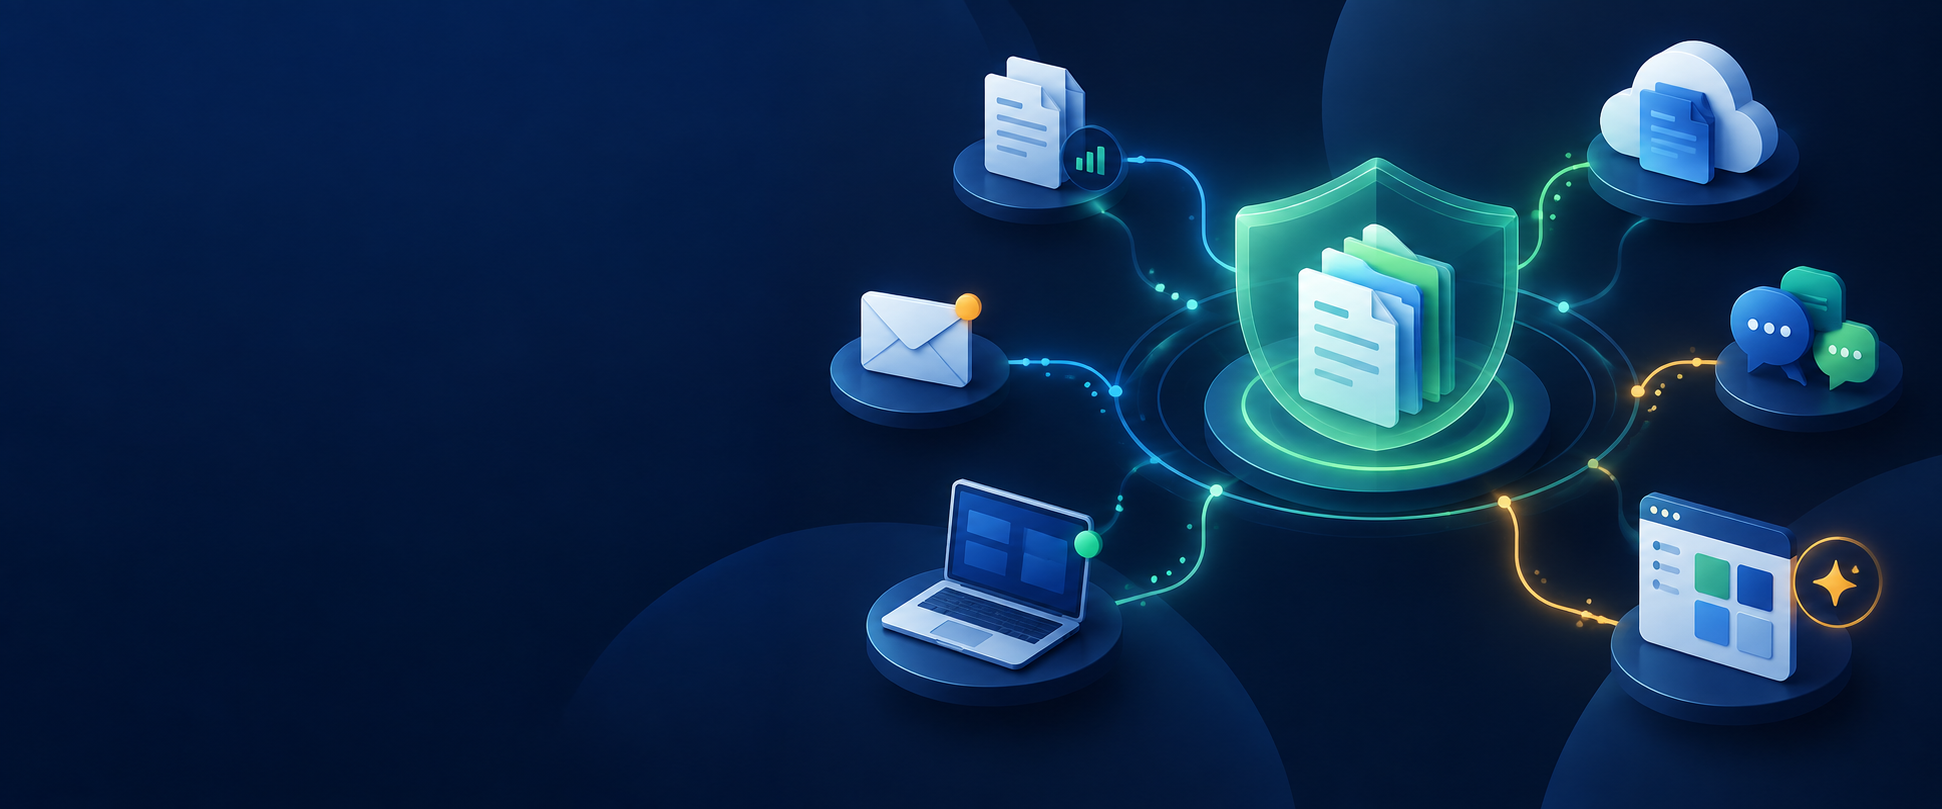
Current Microsoft Purview DLP coverage includes Microsoft 365 services such as Exchange, SharePoint, OneDrive, and Teams, plus supported endpoint devices and additional connected sources. Availability, prerequisites, and supported conditions vary by location. Use Microsoft's current DLP overview and DLP policy reference during design.
Map scenarios to workloads
Exchange Online
Use Exchange DLP for sensitive content in email and supported attachments. A scenario might detect customer identifiers sent to an external recipient, show a policy tip, permit a justified override for approved processors, and alert on high-volume matches.
SharePoint and OneDrive
Use these locations to evaluate stored files and sharing activity. Scenarios often focus on sensitive items shared outside the organization. Remember that evaluation and user-facing policy tips may not be instantaneous, so test the actual user journey.
Teams
Teams DLP can evaluate supported chat and channel messages. Files shared through Teams are stored in SharePoint or OneDrive, so message protection and file protection involve different locations.
Devices
Endpoint DLP extends controls to supported devices. It can audit or restrict activities involving sensitive items, including transfer to removable media, printing, clipboard actions, network shares, browser uploads, and supported paste scenarios. Device onboarding, platform support, browser configuration, and policy prerequisites must be validated before rollout.
Cloud and web destinations
Microsoft continues to expand controls for managed and unmanaged cloud applications, browsers, network activity, and AI services. Some capabilities may be in preview. Treat preview status, licensing, coverage, and operational support as design inputs rather than assuming every tenant has the same controls.
Prerequisites before policy design
Confirm the following:
- required subscriptions and feature licenses
- administrative roles and separation of duties
- audit logging and evidence retention
- supported users, devices, browsers, workloads, and file types
- label availability and publication
- business owners and exception approvers
- a controlled test population and representative test content
- a service desk path for user questions
Licensing changes and differs by capability. Check Microsoft's current service descriptions and the licensing section of each feature page instead of copying a static license assumption into policy design.
The next part turns this model into a safely deployed DLP policy.