Data Loss Prevention
Protect sensitive data wherever people communicate, collaborate, and share information.
Start with one real journey
Follow one piece of sensitive data.
Choose a real record, document, or message and trace it from creation to review. This turns DLP from a product discussion into a set of places and actions your team can protect.
Create
A person, form, document, or business system creates sensitive information.
Use
People and applications view, edit, copy, process, or export it.
Share
It moves through email, chat, links, guests, and collaboration spaces.
Store
It rests in cloud services, repositories, devices, and business applications.
Review
Events are investigated, exceptions are checked, and controls are improved.
Access
Who can reach it?
Movement
Where can it go?
Response
What should happen when risk appears?
Where DLP applies
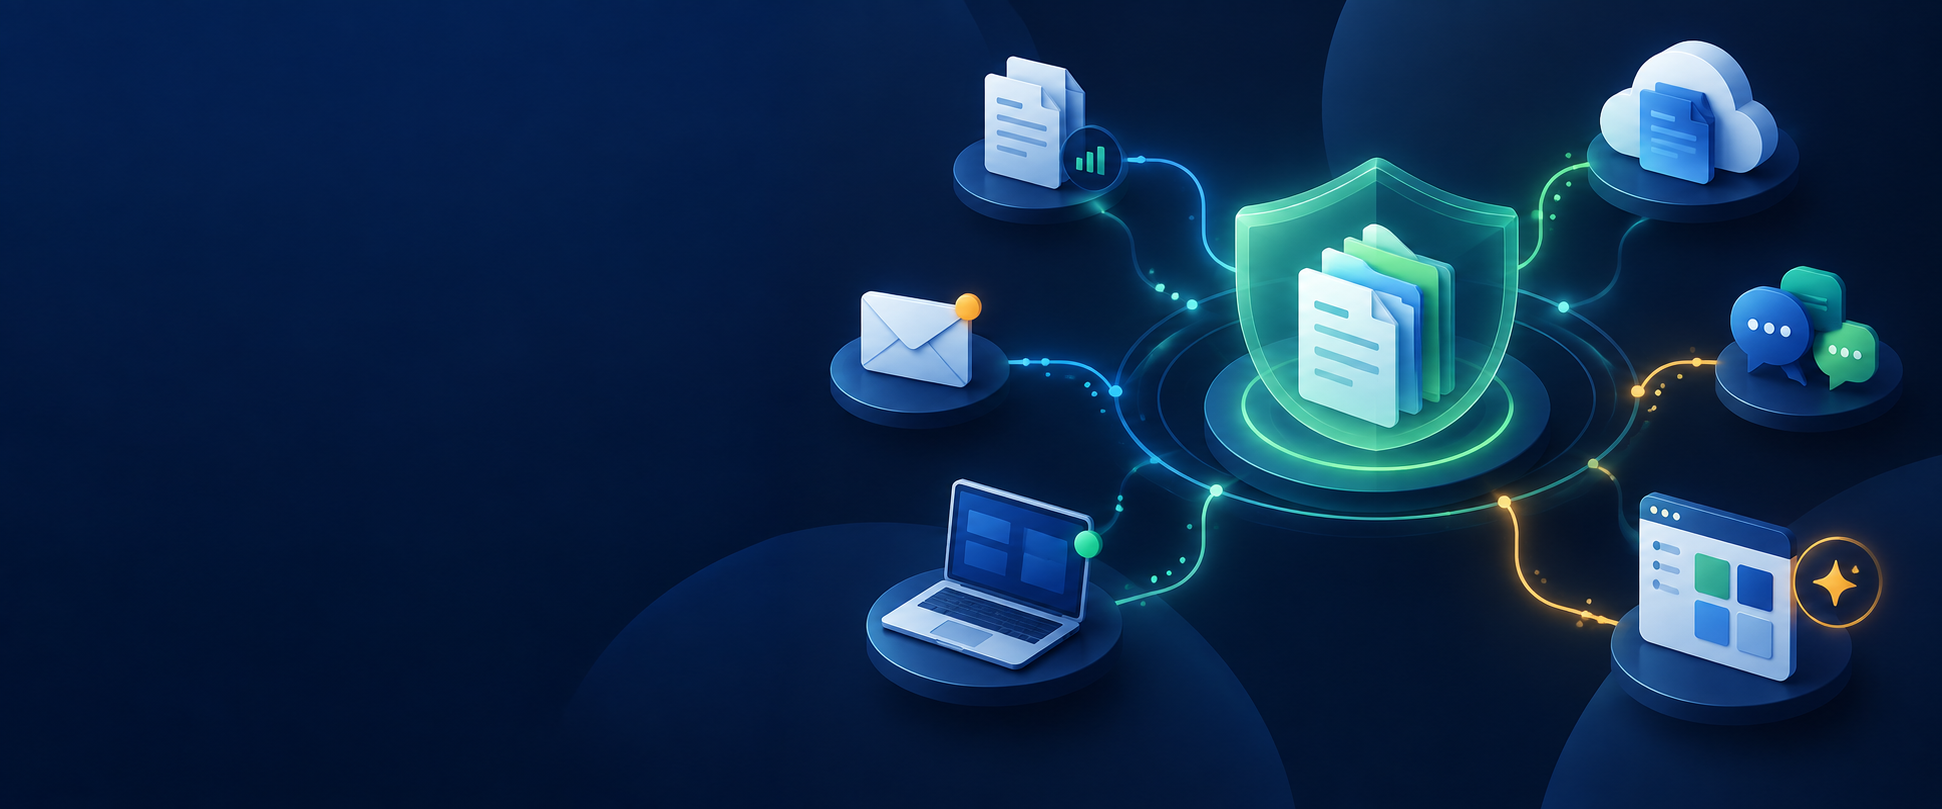
Sensitive data moves through many channels
Messages and attachments sent inside or outside the organization.
Cloud files
Shared documents, drives, repositories, and external links.
Collaboration
Teams, Google Chat, shared workspaces, and everyday teamwork.
Devices
Managed and unmanaged endpoints, removable media, printing, copy, and browser activity.
Business applications
SaaS platforms, line-of-business systems, integrations, and other destinations.
AI and AI applications
Prompts, file uploads, generated content, plugins, and data shared with AI services.
Continue when you are ready
Explore the DLP guidance
Choose your DLP path
Answer two practical questions and go to the guidance that fits your environment.
Open PathfinderUnderstand your data exposure
Build a shared view of sensitive data, leakage paths, and protection layers.
Open overviewNeed Guidance
Choose Microsoft 365, Google Workspace, or Sekurzen Guard guidance.
Open guidanceFAQs & Decision Support
Find practical answers about fit, cost, coexistence, and pilots.
Open FAQs