Think in data states and user actions
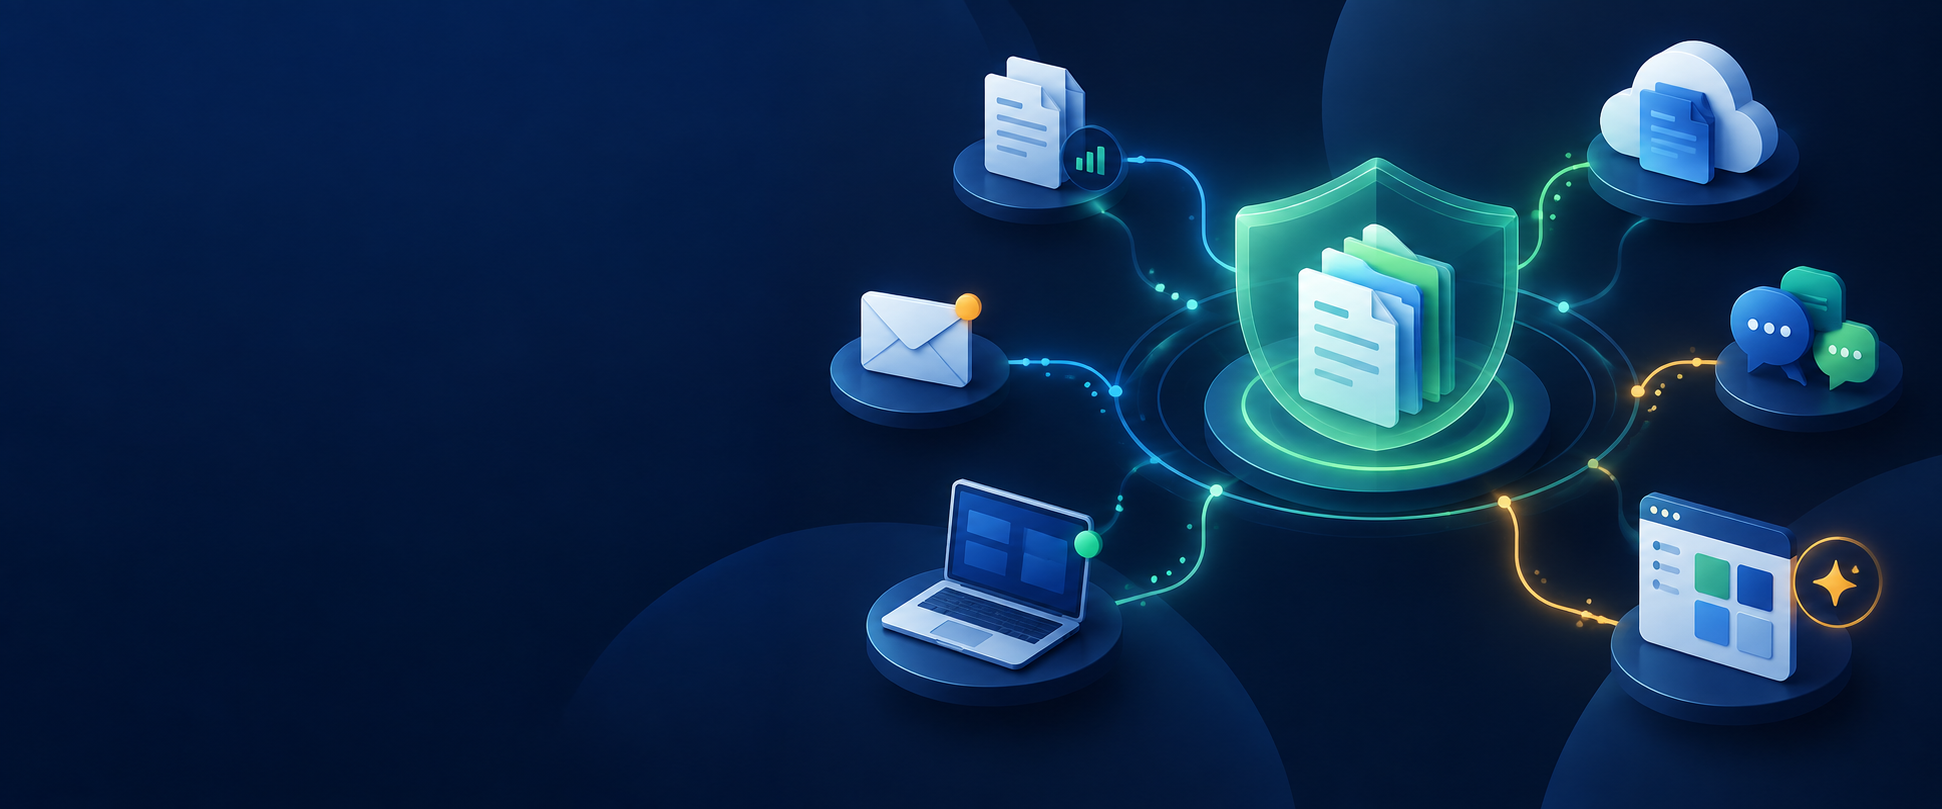
Sensitive data can be exposed while stored, while moving, or while a person or process is using it.
- Data at rest: Files in SharePoint, OneDrive, endpoints, databases, backups, archives, and cloud storage.
- Data in motion: Email, chat, file transfer, synchronization, APIs, uploads, and network traffic.
- Data in use: Copying, printing, screen capture, browser paste, export, local processing, and AI prompts.
A repository permission protects data at rest, but it may not protect a downloaded copy. Email encryption can protect a message in transit, but it does not correct an unauthorized recipient. Controls must follow the full path.
Common leakage paths
Email and messaging
People can select the wrong recipient, use autocomplete without checking, attach the wrong file, forward a message externally, or place sensitive content directly in the message body. Collaboration chat creates similar risks, especially when guests or external federation are present.
Oversharing and public links
A file can remain in an approved service but still be leaked through a link that is anonymous, organization-wide, or accessible to an outdated guest. Permission inheritance and membership changes can make exposure difficult to see.
Endpoints and removable media
Downloads create local copies that can move to USB storage, network shares, printers, personal cloud applications, or unmanaged browsers. A compromised endpoint can also provide an attacker with access that appears to come from a legitimate user.
Cloud applications and shadow IT
Users often adopt consumer file-sharing tools, note-taking services, converters, and browser extensions to finish a task quickly. These services may retain uploaded content or use it in ways the organization has not reviewed.
Generative AI
Prompts, pasted text, and uploaded files can disclose source code, personal data, contracts, incident details, or strategic material. The risk depends on the service, tenant controls, contractual terms, and how submitted content is handled. An AI-specific rule should distinguish approved enterprise services from unmanaged destinations.
Privileged and departing users
Administrators and employees with broad access can collect unusually large volumes of data. Risk may increase around role changes, notice periods, investigations, or unusual access patterns. Monitoring should be proportionate and governed to protect employee privacy.
Automated integrations
Service accounts, connectors, scripts, sync tools, and APIs can transfer data at scale. These paths receive less user-facing attention but can create a larger exposure than a single email.
Assess the scenario, not just the channel
Use four factors to prioritize a leakage path:
- Impact: How harmful would exposure be?
- Likelihood: How often does the action occur, and how easy is misuse?
- Exposure scale: Could one event disclose one record or an entire data set?
- Current control strength: Is the path blocked, monitored, logged, or invisible?
For example, printing may be low frequency but high impact for a merger document. External email may be frequent and necessary, so a hard block on every sensitive match could be unworkable. The response must reflect both the data and the workflow.
Separate mistakes, misuse, and compromise
The same action can have different causes:
- Accidental: A person selects the wrong recipient or link setting.
- Convenience-driven: A person bypasses an inconvenient process to finish legitimate work.
- Malicious insider: An authorized user intentionally takes information.
- Compromised identity or device: An attacker uses valid access.
- Automated error: A workflow sends data to the wrong destination at scale.
User education helps with mistakes. It is less effective against compromised accounts or deliberate theft. Strong programs combine prevention, behavioral signals, access controls, endpoint security, and investigation.
Create a channel-control matrix
For every priority data set, record the allowed and prohibited actions across email, collaboration, endpoints, browsers, cloud apps, removable media, printing, and APIs. Then identify:
- the preventive control
- the detective control
- the evidence available for investigation
- the exception path
- the owner who accepts residual risk
This matrix turns a vague goal such as "stop data leakage" into a set of testable requirements. The next part organizes those requirements into layered protection.